Your customers brought an agent.
Your customers didn't wait for you to have a plan. Most of the agents on your site today are personal agents like Muse, here to buy something on a real customer's behalf. The opportunity is letting them through. The work is deciding which agents you trust and what each one is allowed to do.
Live Oct 27: Personal AI Is Already Your Customer. Register →The question is no longer "is this a bot?"
For a decade, the question was bot or human. Now both sides are bots, and the question that decides whether you grow revenue or lose it is a different one: is this agent authorized to do what it is trying to do?
Verified is not authorized.
An agent can present a valid signature and still attempt something you never allowed.
Policy turns on the action.
Browsing a catalog is not moving money. Score what the agent is trying to do, not only the session it arrived in.
What an agent can do depends on what it attempts
Illustrative. Where you draw the lines is your decision.
35x more Muse in four weeks.
Meta shipped Muse free to US consumers on 8 September. In the four weeks that followed, Muse sessions across our network grew 35x, and Muse now outpaces every other agent we track. This is not a projection. It is what our customers' login pages recorded.
Nobody asked permission. There was no API to integrate and no standard to adopt. The agent opened a browser and used the login form that was already there, which means this arrived at your business whether or not you had a plan for it.
Three populations. One signature each.
Catching all three takes device, behavioral, and adaptive signals working together.
Self-disclosing good agents
Verified agents that sign their requests. Cryptographic signatures. Web Bot Auth.
They cooperate. They publish IP ranges and sign HTTP headers. Standards bodies and CIAM vendors are racing to serve this cohort.
Caught by: disclosure standards. The easy population.
What you decide: which verified partners get through, and to which flows.
Non-disclosing good agents
Muse. Instinct. Claude computer use. ChatGPT agent mode. Local agents on real laptops.
Operating on behalf of a real user, for legitimate purposes. They will never declare. The signal that gives them away is behavioral, not network.
Caught by: behavioral biometrics + Device ID.
What you decide: which flows these agents can reach, and what they can do there.
Malicious agents
Account takeover. Fake accounts. Payment fraud. Scraping.
Cloud-hosted at scale. Spoofed devices, almost always impersonating Mac Chrome. Their tell is the spoofing itself: fingerprint mismatches and residential proxies.
Caught by: device spoofing detection + PoW.
What you decide: stop them, and make every attempt cost more.
Population Two is the one nobody planned for. It is also the one arriving by the hundreds of millions with a customer attached.
Where an agent runs decides how you catch it.
Populations tell you what it's for. Categories tell you where it runs, and each leaves a different fingerprint.
Cloud-hosted agents
ChatGPT. Anthropic API. Cloud-deployed bots.
- Spoofed devices. Almost always impersonate Mac Chrome.
- Cloud infrastructure. Data-center ASNs, residential proxies.
- Fingerprint mismatches. OS, UA, WebGL, canvas inconsistencies.
Device intelligence and Proof of Work invert the unit economics of cloud-scale automation.
Local browser agents
Atlas. Perplexity Comet. Custom Chromium forks.
- Static quirk detection. Claims Chrome, executes a forked engine.
- Chromium fork signals. Build flags, V8 timings, render anomalies.
- Behavioral biometrics. Click cadence, mouse trajectory shape.
Static quirk analysis and behavioral biometrics surface forked browsers even when the fingerprint looks clean.
Local OS-level agents
OpenClaw. Claude Cowork. Controllers driving real Chrome.
- Vision, reasoning, action loop. Screenshot, infer, click sequencing.
- Timing anomalies. Inhuman pauses, no fluid micro-motion.
- Device ID and biometrics. Real device, non-human interaction.
Persistent device identity and behavioral biometrics surface the agent even on a real device.
Two agents. Two ways of failing to be a person.
Neither announced itself. Both were caught by the movement alone.
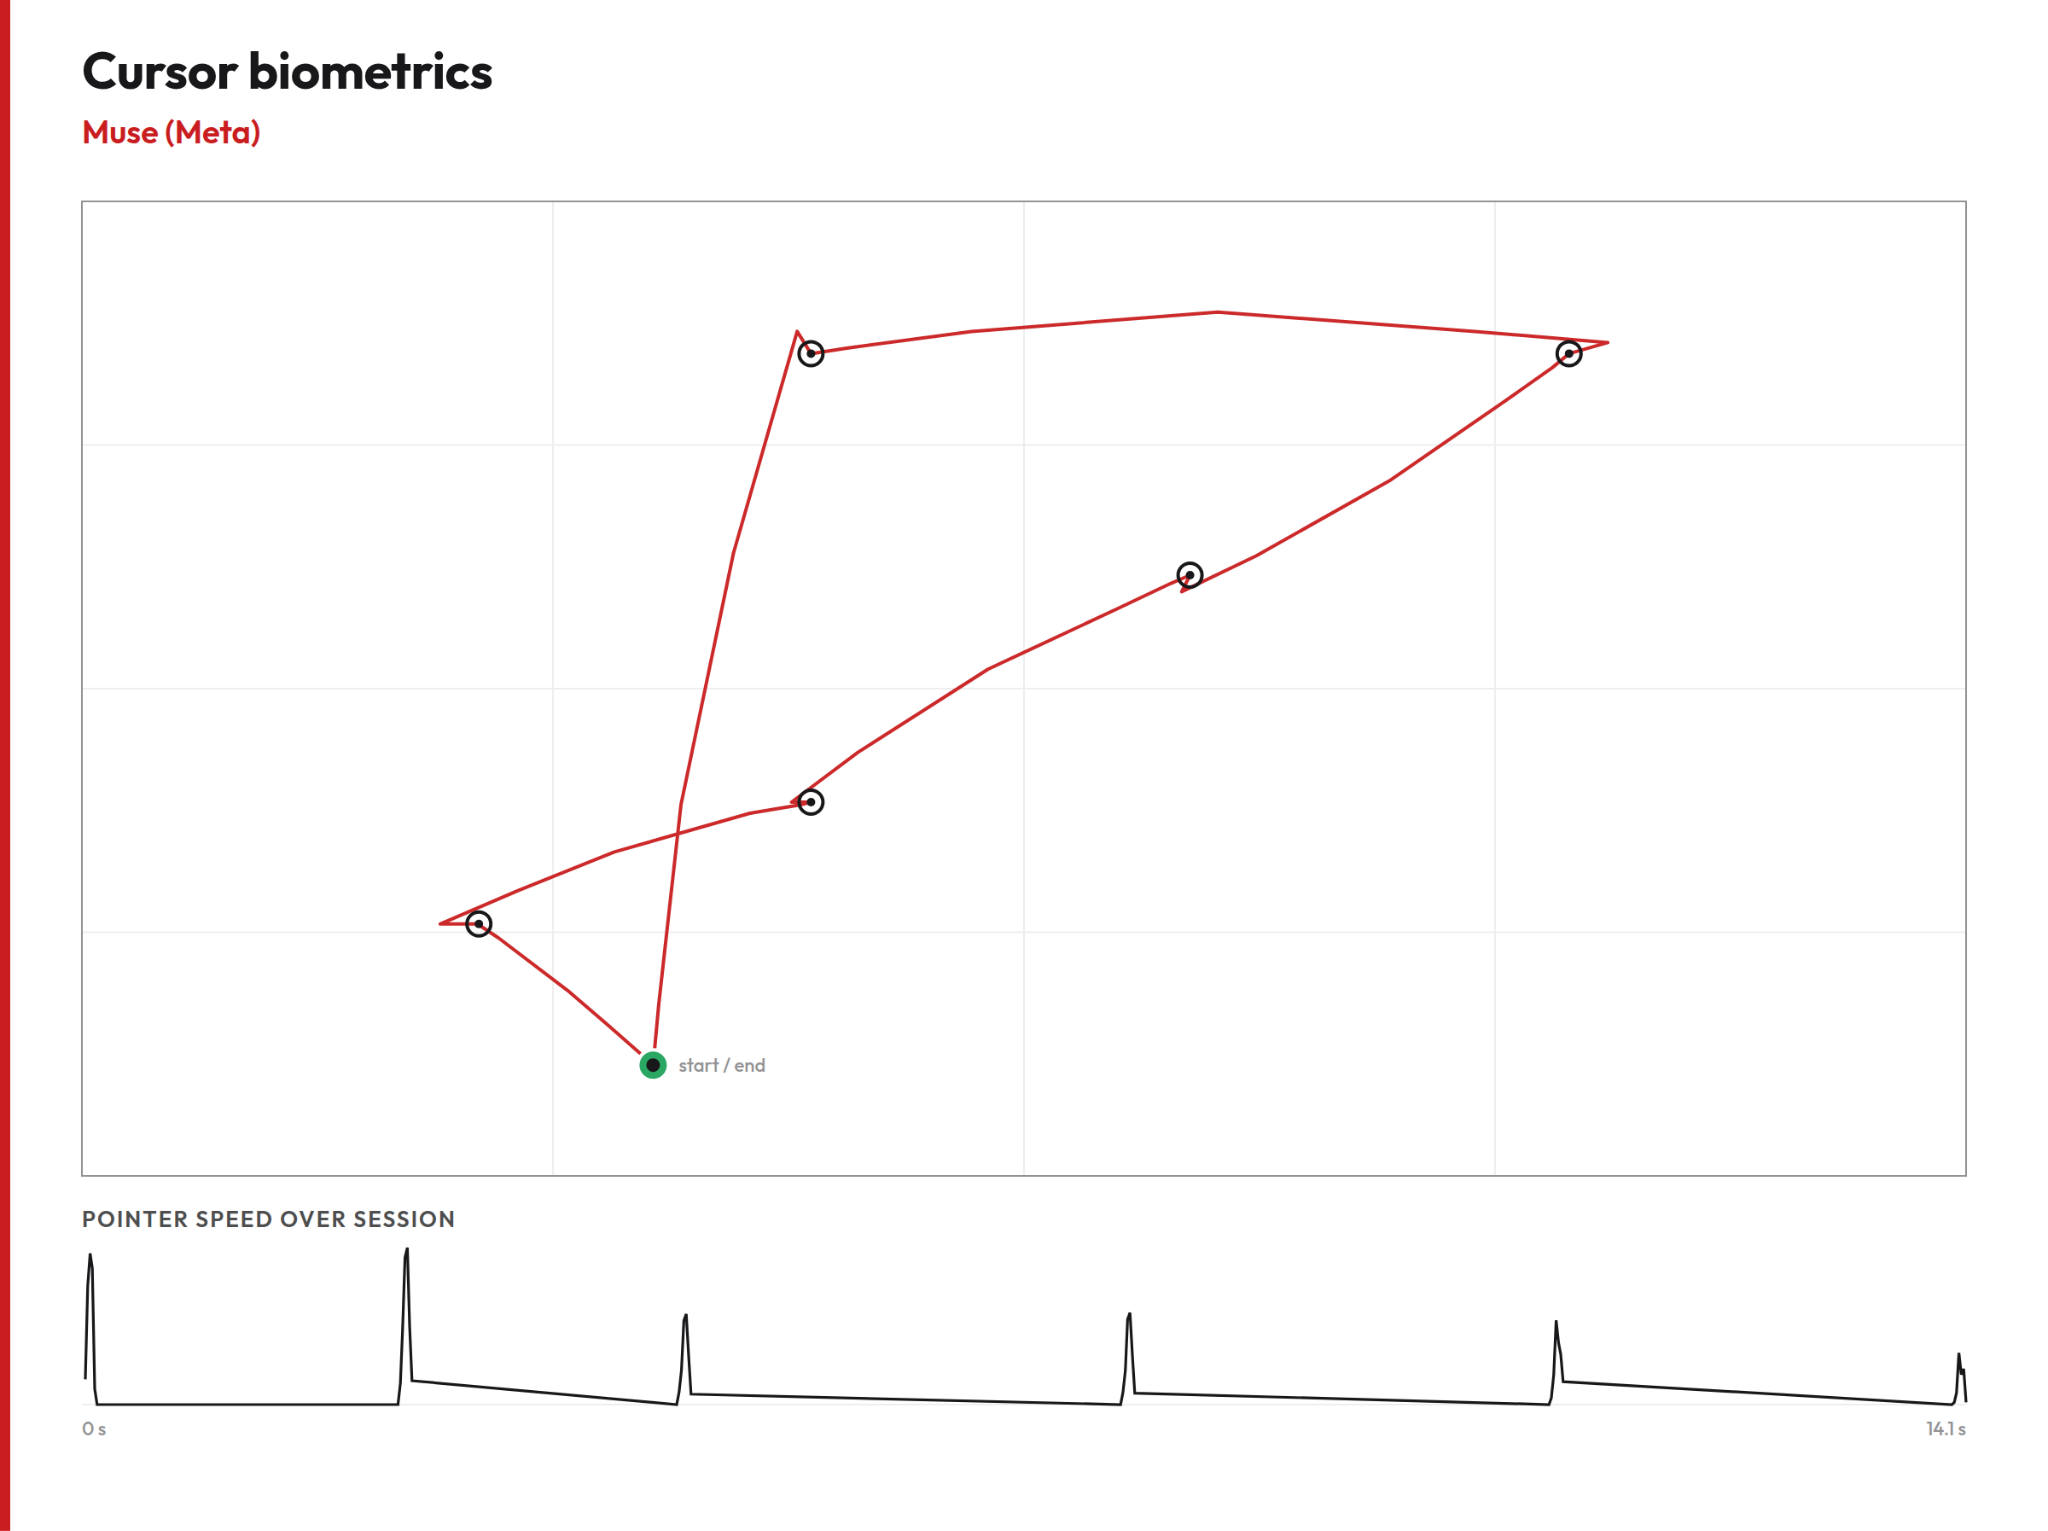
Muse: the simulated hand
Muse tries to move like a person, and the attempt is the tell. The path wanders and doubles back, but the speed trace shows the same sawtooth spike again and again: instant acceleration, smooth decay, repeated with a regularity no hand produces.
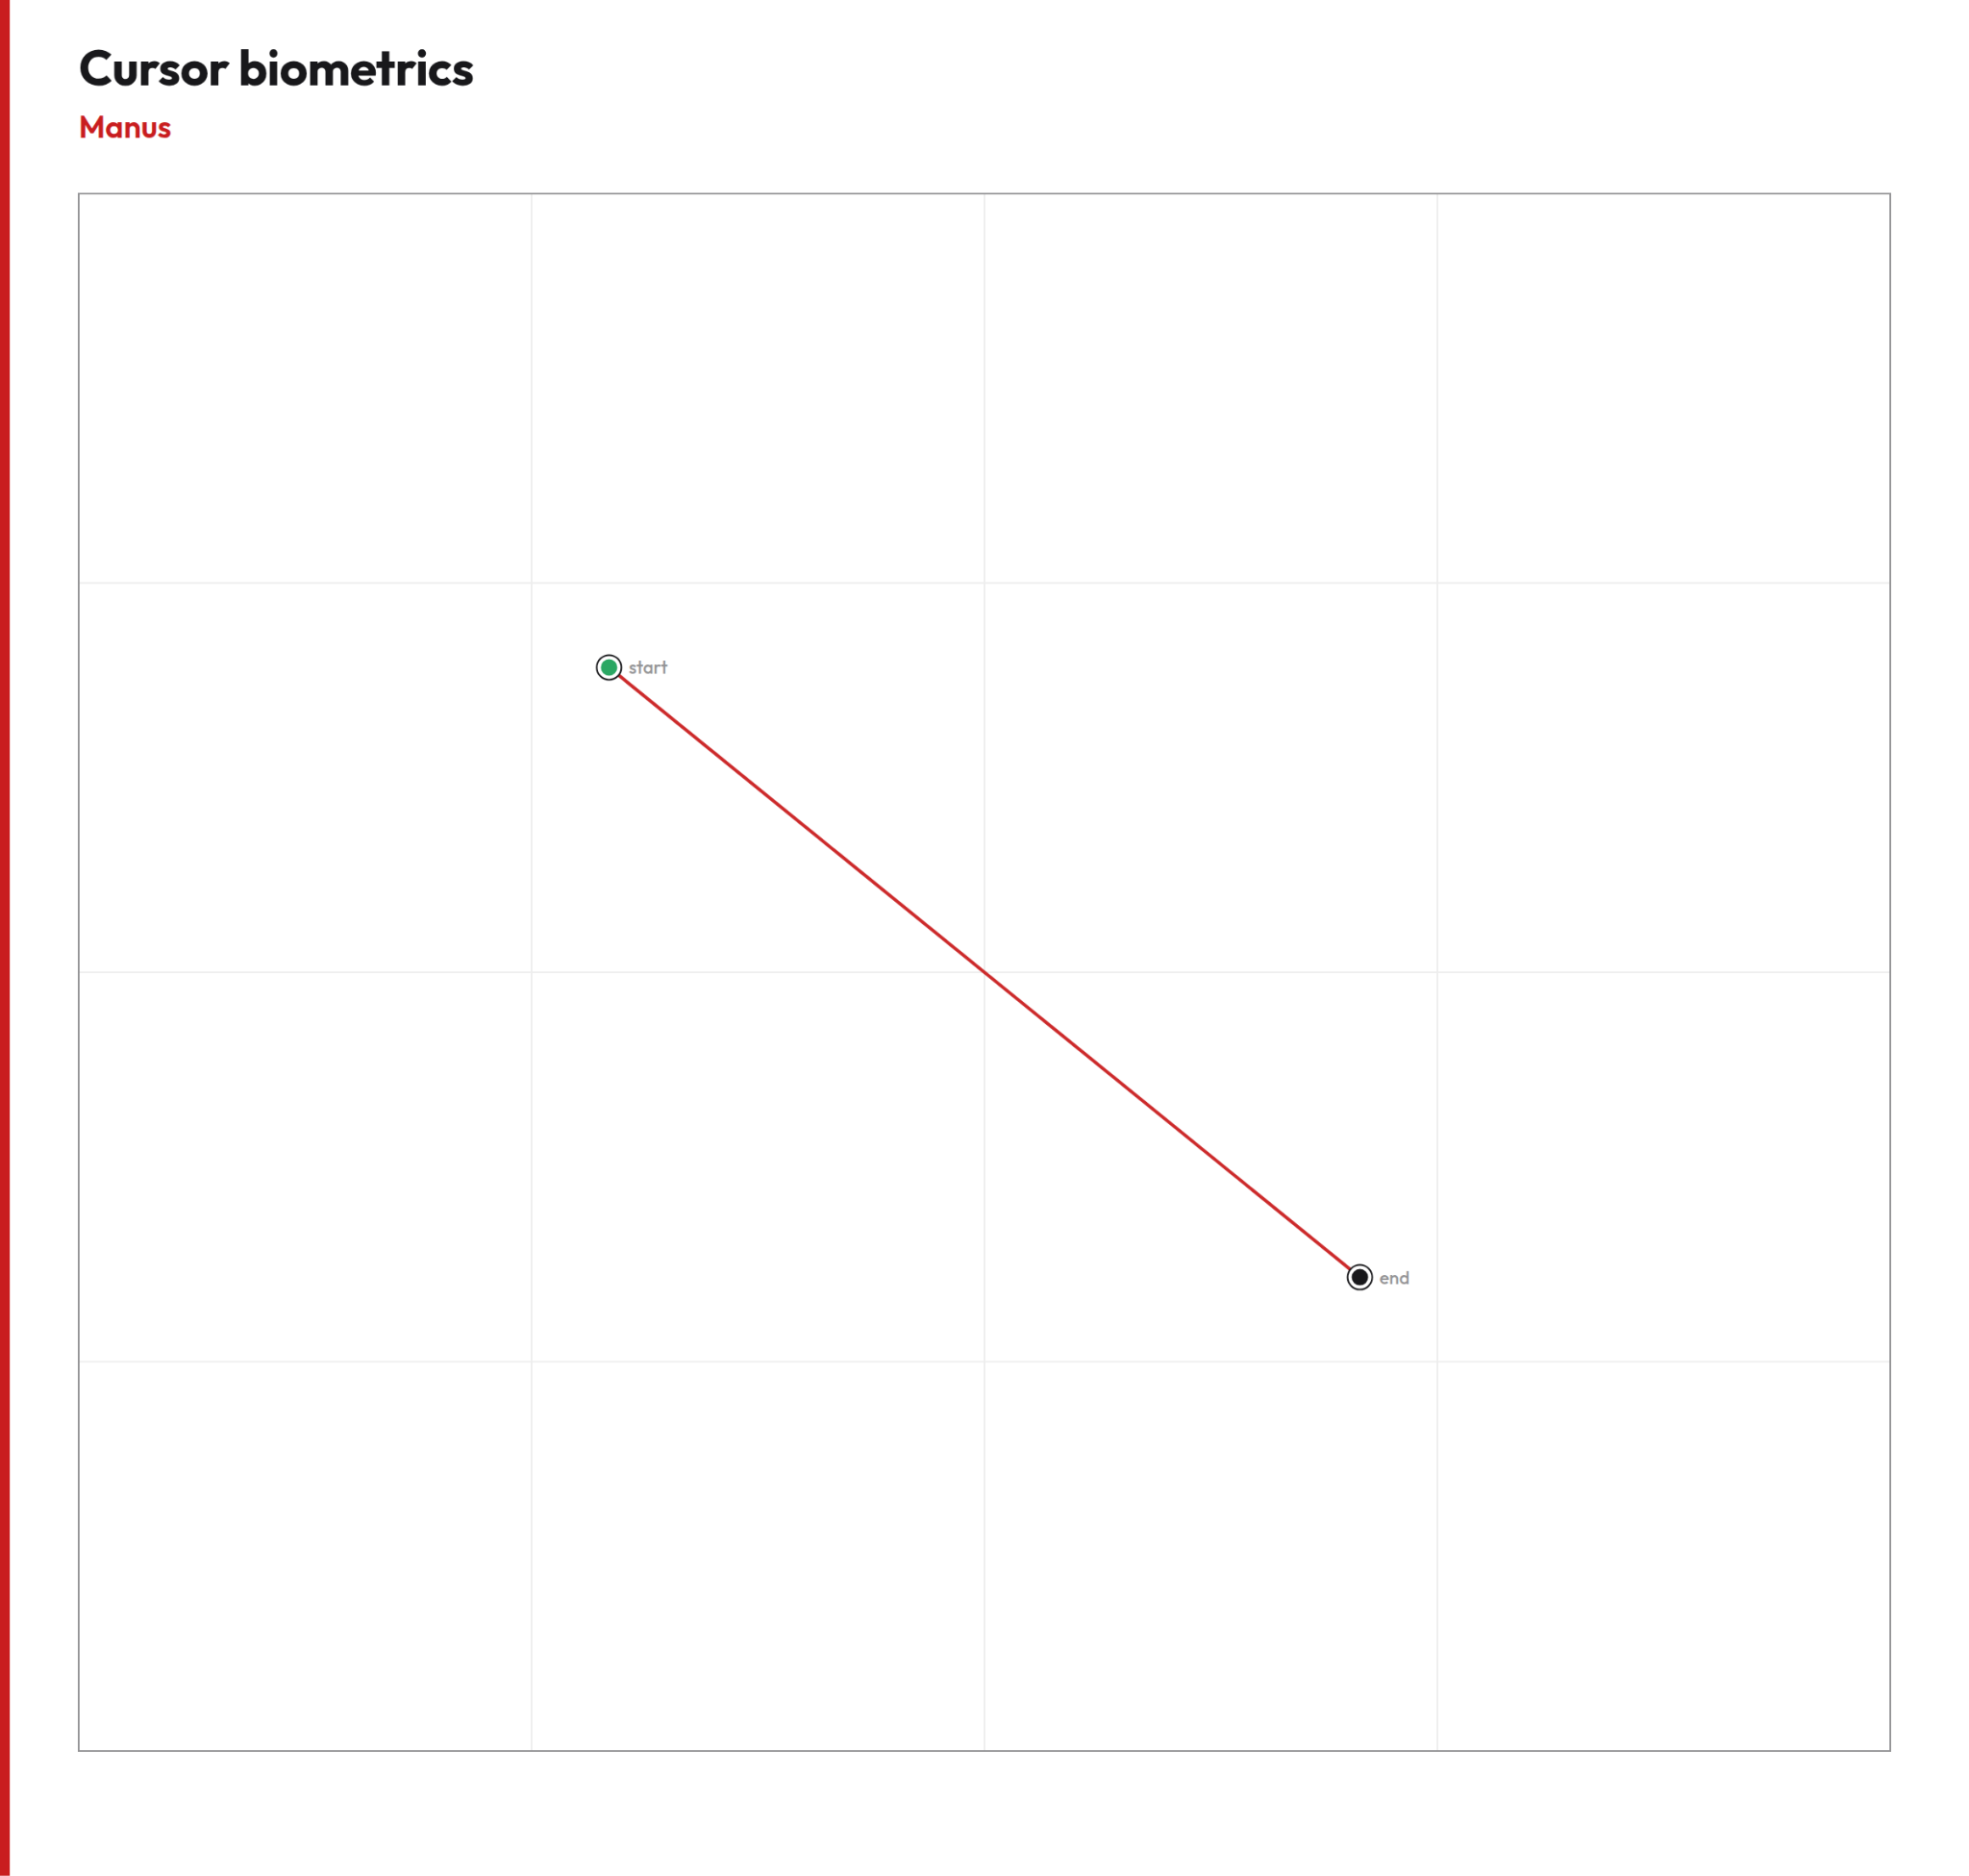
Manus: no hand at all
Manus doesn't simulate anything. Start point to end point, one straight line, no correction and no overshoot. A person reaching for a target never travels in a perfect line, and never arrives without adjusting.
This is what Population Two looks like on a real device, with real credentials, at a login page that has no other reason to be suspicious.
Knowing it's an agent is the easy half
Detection answers one question: is something automated here. That answer is not much use on its own, because it is true of the customer's shopping assistant and the credential stuffing run in equal measure. Acting on detection alone is how businesses end up blocking the traffic they wanted.
Classification answers the question that follows: which agent is this, who is it working for, and is what it's attempting something you allow. That takes more than one signal source. Device intelligence places the machine. Behavioral biometrics read the hand. Network signals show where it runs. Adaptive challenges test what it can actually do. Read together, they resolve a session into something you can make a decision about.
Arkose Titan carries all four.
One agent name. One undifferentiated block of traffic. Allow it all or block it all, and most teams choose block, because there's nothing to tell the sessions apart.
Persistent device identity resolves the individual virtual machine behind each session, so one customer's Muse is a different object from another's. Your existing risk logic applies to agent traffic the way it already applies to people.
You never have to turn away good customers because one of them has a compromised agent.
Arkose Titan carries the agent's identity across sessions, so your policy can reflect history, not only the current request.
Most of them don't identify themselves. Each leaves a trail.
Every one of these is a customer trying to get something done. Naming them is how you let them.
Let the agents buy. Make the attackers pay.
Let the good agents buy
Agentic commerce only works if the agent can finish the transaction. Block it and the sale doesn't happen, and it never shows up as a loss, because the session simply ends. Visibility and classification let you open the door deliberately instead of leaving it shut by accident.
Make the attackers pay
The sessions trying to abuse you run on the same tooling. Adaptive challenges a model can't solve and compute costs that scale with risk make the attempt uneconomic, so the attacker gives up or hands control back to a human. Invisible to the customers you want.
One classification decision drives both, on one platform: Arkose Titan.
Four controls, built for a human at the keyboard.
Device trust.
The fingerprint belongs to the agent, not your customer. Hardware, IP, and geography you've never seen. It reads as takeover when someone is just buying something.
Velocity and geography.
Geo-impossibility rules assume a body in a place. A model can learn your threshold and sit underneath it.
Behavior.
Still separates agent from human. Never separates a customer's agent from a fraudster's.
Authentication.
Credentials vaulted and injected at point of use. No typing, and in some markets a single consent sets a standing mandate with no fresh step-up.
Block this without deciding to, and your bot defense is making a revenue call on your behalf. Arkose Titan puts that decision back with you.
Treat IP as context, not identity.
Hosted agents used to come from a few cloud and edge networks, so network origin was a cheap first filter. That no longer holds. In October, Muse began arriving through US and UK residential and mobile carriers, between a quarter and a half of Grok Bot's new-image sessions now exit through residential ISPs, and about half of Instinct's sessions arrive on residential and mobile networks. The same residential IPs carry legitimate agents and abuse, so neither an IP allowlist nor an IP blocklist separates them, and a policy built on IP reputation misses agents on clean residential connections.
Key your policy off the agent Arkose Titan identifies and its device identity. If you only want to stop a specific misuser of an agent, scope the rule to the agent plus the device.
We assume every agent detection will drift.
Agent builds, networks and disguises change constantly, and some changes look designed to make agents harder to identify. So the operation is built around finding drift fast.
Agent canary
We run each major agent ourselves on a schedule and compare what we see with a known baseline, so we can tell what moved and whether the agent or our detection changed.
Production monitoring
Continuous checks on every agent detection flag volume that goes quiet, erodes, or spikes.
Runbook-driven repair
Researchers isolate what changed, recapture the agent, validate against known-good and known-bad traffic, and release. New detections ship as monitor-only first.
Durability by design
Detections combine many independent device, network and behavioral characteristics, so no single value an agent can change breaks them.
Each fix ships once to every customer, with no code changes on your side.
Most teams start with visibility, then set policy.
Today, most buyers want to see which agents are on their site first, starting with Muse, and many block all agents while they do. That is a reasonable start. Arkose Titan is built for what comes next: deciding flow by flow which agents to let through. Blocking every agent for good turns away customers who chose to shop through one.
Start with a guided 7-day proof of value.
Frequently Asked Questions
What is agentic AI, and why does it matter for online security?
Agentic AI refers to AI systems like Muse, Instinct, Comet and Atlas that act autonomously on the web such as logging in and completing purchases on someone's behalf. Since malicious automation can look nearly identical technically, detection alone isn't enough anymore.
Are all AI agents a threat to my business?
No. AI agents fall into three populations: self-disclosing good agents that publish their identity and follow disclosure standards, non-disclosing good agents acting on a real customer's behalf, and malicious agents.
Why can't traditional bot detection tell good AI agents from bad ones?
Traditional detection answers "bot or human?" and both sides are now bots. Legitimate and malicious AI agents use the same automation technology with similar interaction patterns, so the real question is intent, not automation.
How is classifying an AI agent different from just detecting one?
Detection only confirms that traffic is automated. Classification evaluates an agent's intent to determine whether that automation is authorized, unknown or malicious, so it can be treated accordingly instead of blocked outright.
What is agent orchestration?
Agent orchestration is how you decide which AI agents to trust and what each one can do on your site. You set the policy by agent and endpoint. Arkose Titan identifies the agent, including agents that don't announce themselves, and applies your policy while the interaction is happening.
Is agent orchestration about building or running my own agents?
No. It covers agents that arrive from outside your business, such as a customer's shopping assistant, on your login, signup, checkout, and account flows. It is not a framework for building or running your own agents, and it is not workforce agent management.
Should I block all AI agents?
Many teams start by blocking all agents while they get visibility. The point is to have visibility and control first, then decide flow by flow. Blocking everything for good means turning away customers who have chosen to shop through an agent.
What is Muse, and why does it matter for my site?
Muse is Meta's personal AI agent. Meta shipped it to every US consumer on 8 September, it doesn't identify itself, and it acts for your customers on your login, signup, and checkout flows. Arkose Titan identifies it and lets you decide what it can do.
Why can't I just block agents by IP address?
Most agents now arrive on residential and mobile networks that also carry legitimate customers and abuse, so an IP block or allowlist can't tell them apart. Arkose Titan keys decisions off the agent it identifies and its device identity, and you can scope a rule to the agent plus the device.